All Categories
Featured
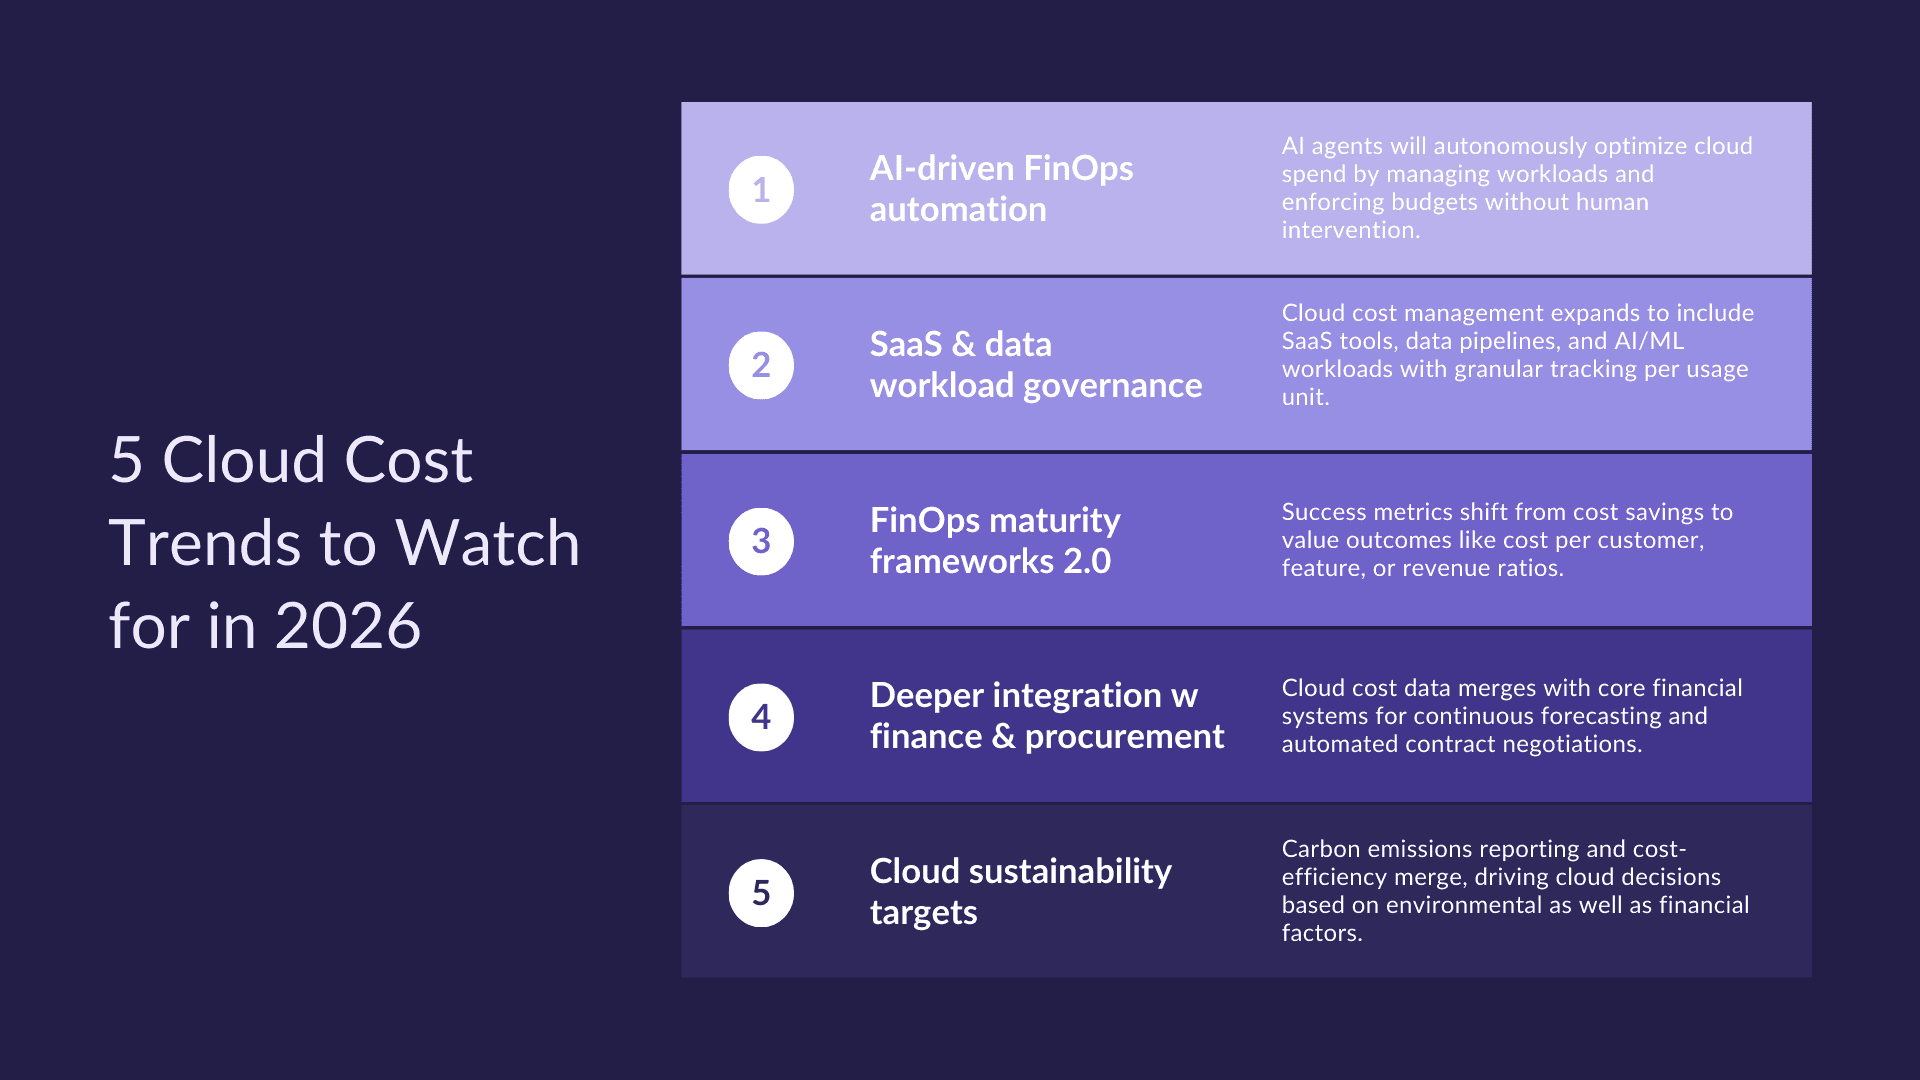
Is Your 2026 Cloud Infrastructure Ready for Efficiency?
Table of Contents
To asses risk Waydev allows you to measure how most likely it is a specific dedicate will cause issues. In this case, there are particular information points that you need to take into consideration, such as the devote's size, how far do the changes spread, along with the changes' depth. Continuous Combination (CI) and Continous Advancement (CD) are vital in today's engineering community because they guarantee that your group provides software in an iterative kind.
Why Infrastructure Metrics Matter for GrowthOur option immediately gathers data from the Continuous Integration and Continous Advancement pipelines and tracks Gitlab repos, enabling you to analyze info without needing any kind of manual input. This is an exceptional way to keep an eye on DevOps performance by focusing on DORA metrics. By automating these processes and measurements, you might have a clear view of how deployment is going, evaluate what effects burn-down rates, what triggers traffic jams, and how to resolve them.
With Waydev's Job Expenses report, you have constant insights on how work is progressing and how things look financially. This allows you to reallocate resources to ship on time or optimize expenses and communicate task status to magnate. When done right, the aligns service requirements with technology processes, making it possible for Engineering Supervisors to enhance efficiency and analyze threats.
IT governance focuses on setting tactical instructions, policies, and oversight. Training needs to cover framework concepts, brand-new policies and procedures, governance functions and duties, and any governance tools or systems being implemented.
Mastering Governance Excellence in Multi-Cloud Systems
More frequent evaluations may be required for fast-changing environments. KPIs to measure effectiveness include IT cost optimization, IT and business strategy positioning, user fulfillment, project ROI, and adherence to service levels. Danger management recognizes risks, assesses effects, and establishes mitigation strategies. It ensures governance effectively addresses details security, catastrophe healing, and regulative compliance.
Reliable IT governance is a crucial part of total organization method and business governance as a governance, risk and compliance (GRC) policy. IT governance manages governance and dangers while preserving compliance with industry and federal government policies. Enhancing IT governance requires the best mix of IT investments, policy and personnel. It assists companies match their IT goals with organization goals.
It is increasingly an element of DevOps groups responsible for IT operations. DevOps groups interact more effectively to create, test and provide software. As organizations increase their IT investments, the importance of a strong IT governance policy boosts. Chief information officers (CIOs) drive IT governance technique alongside other key stakeholders in the C-suite.
Key Methods for Better IT Resource AllocationIn this postWhat is IT governance and why does it matter?Why is reliableIT governance essential for company success?What are the 5 actions to execute efficient IT governance?What are the IT governance best practices that drive results?How does IT governance work for little businesses?Why well-established IT governance is a service advantage Efficient IT governance aligns innovation decisions with company method, controls threat, and guarantees IT resources are utilized efficiently. This guide covers each step in practical detail, along with the structures, tools, and finest practices IT leaders utilize today.
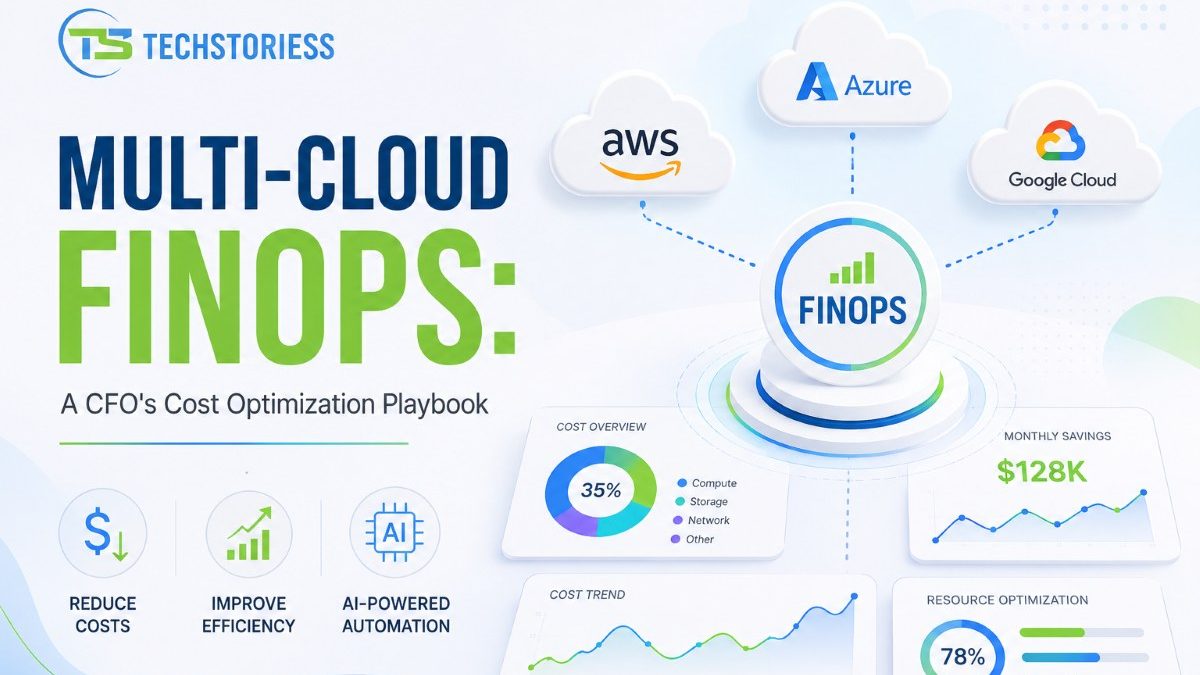
Analyzing Decentralized IT Governance Models for 2026
Assign clear accountability for each governance domain. Structure Main focus Finest fit for IT governance and management, threat control, audit preparedness Large business, controlled markets IT service management aligned to company requirements Organizations with a fully grown IT service function International standards for IT service management and business IT governance Organizations seeking licensed, internationally recognized governance CMMI(Capability Maturity Design Integration)Process improvement ranked on a scale of 1 to 5 Organizations benchmarking and enhancing development or delivery capability COSO (Committee of Sponsoring Organizations of the Treadway Commission)Internal control and business danger management Organizations prioritizing financial controls and scams deterrence CIS( Center for Web Security)Controls Cybersecurity and facilities resilience Organizations reinforcing technical security posture Many organizations combine frameworks. Governance that is not measured does not improve.

Latest Posts
Maximizing IT Metrics for Budgetary Success
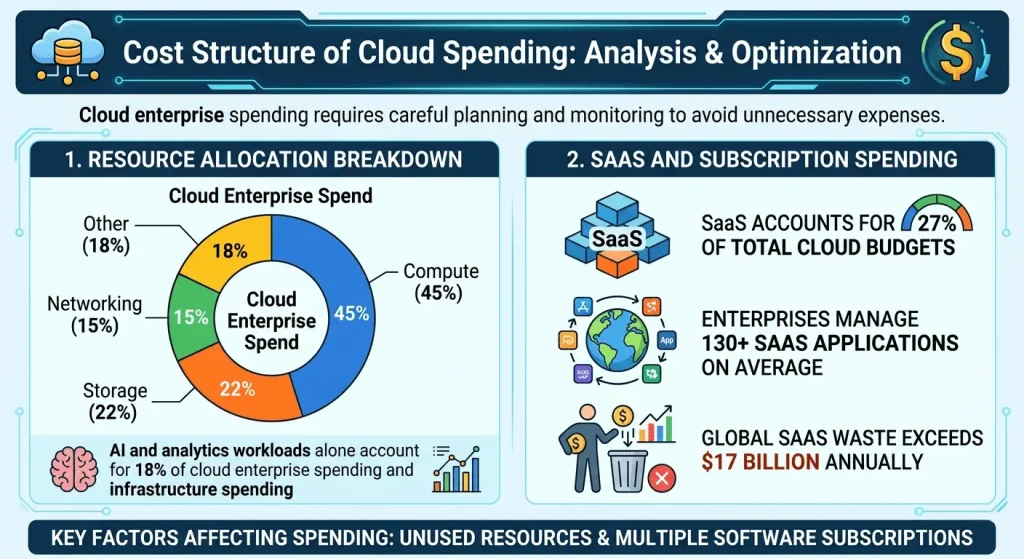
Improving Enterprise Efficiency KPIs Through Advanced Governance
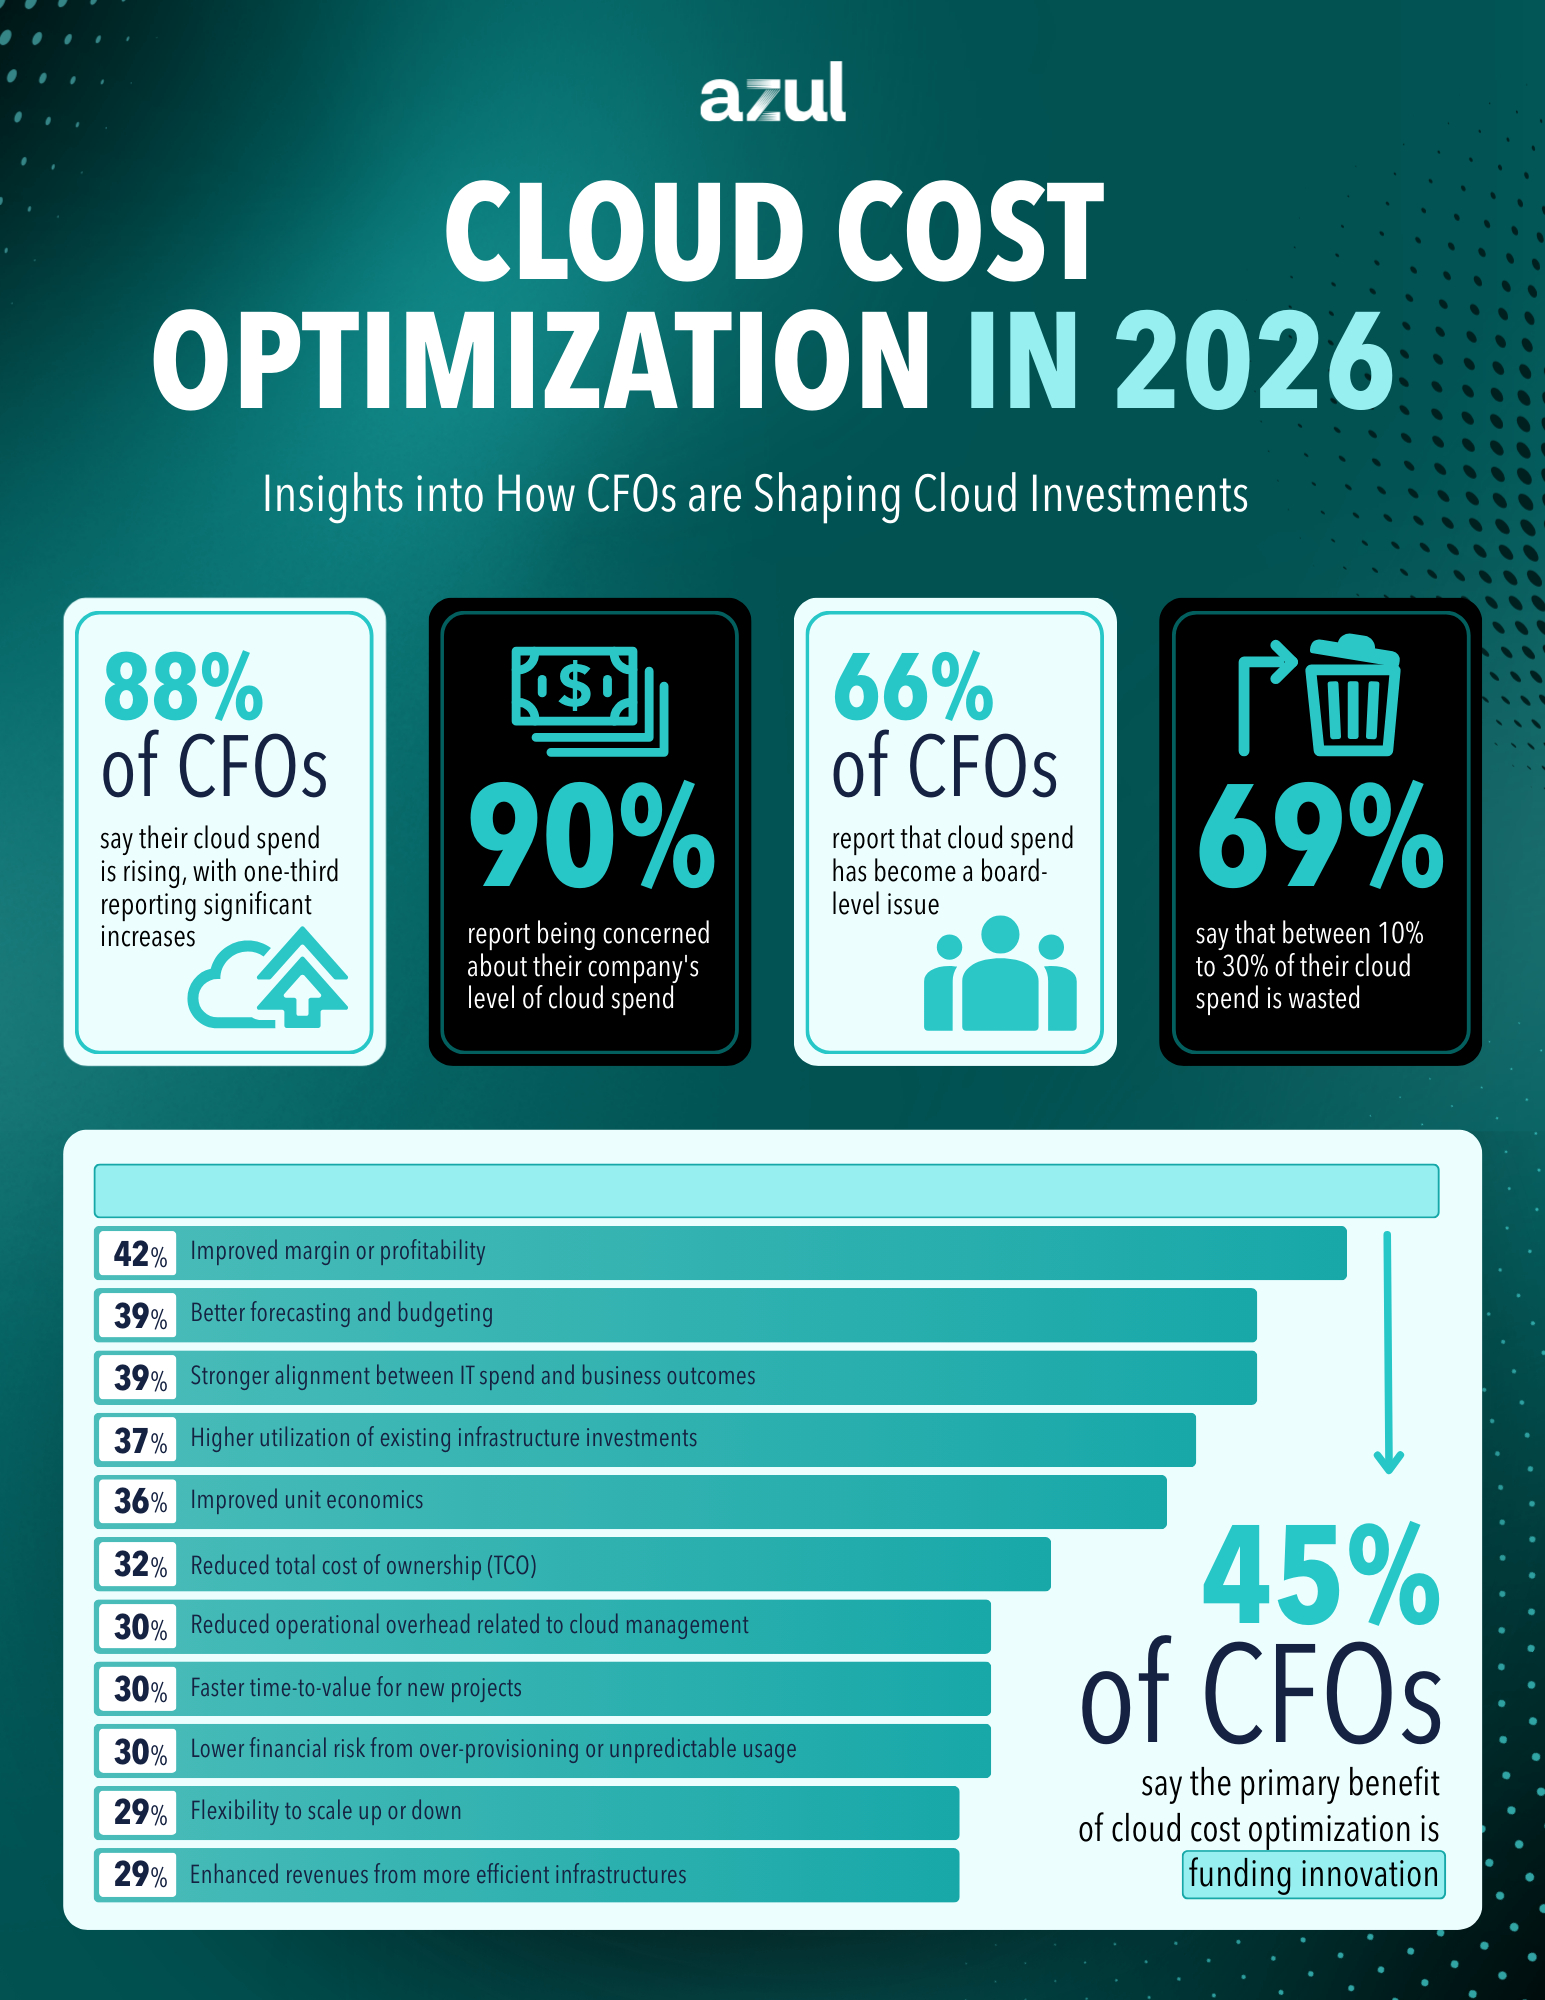
Effective Steps for Reducing Cloud Spend in 2026